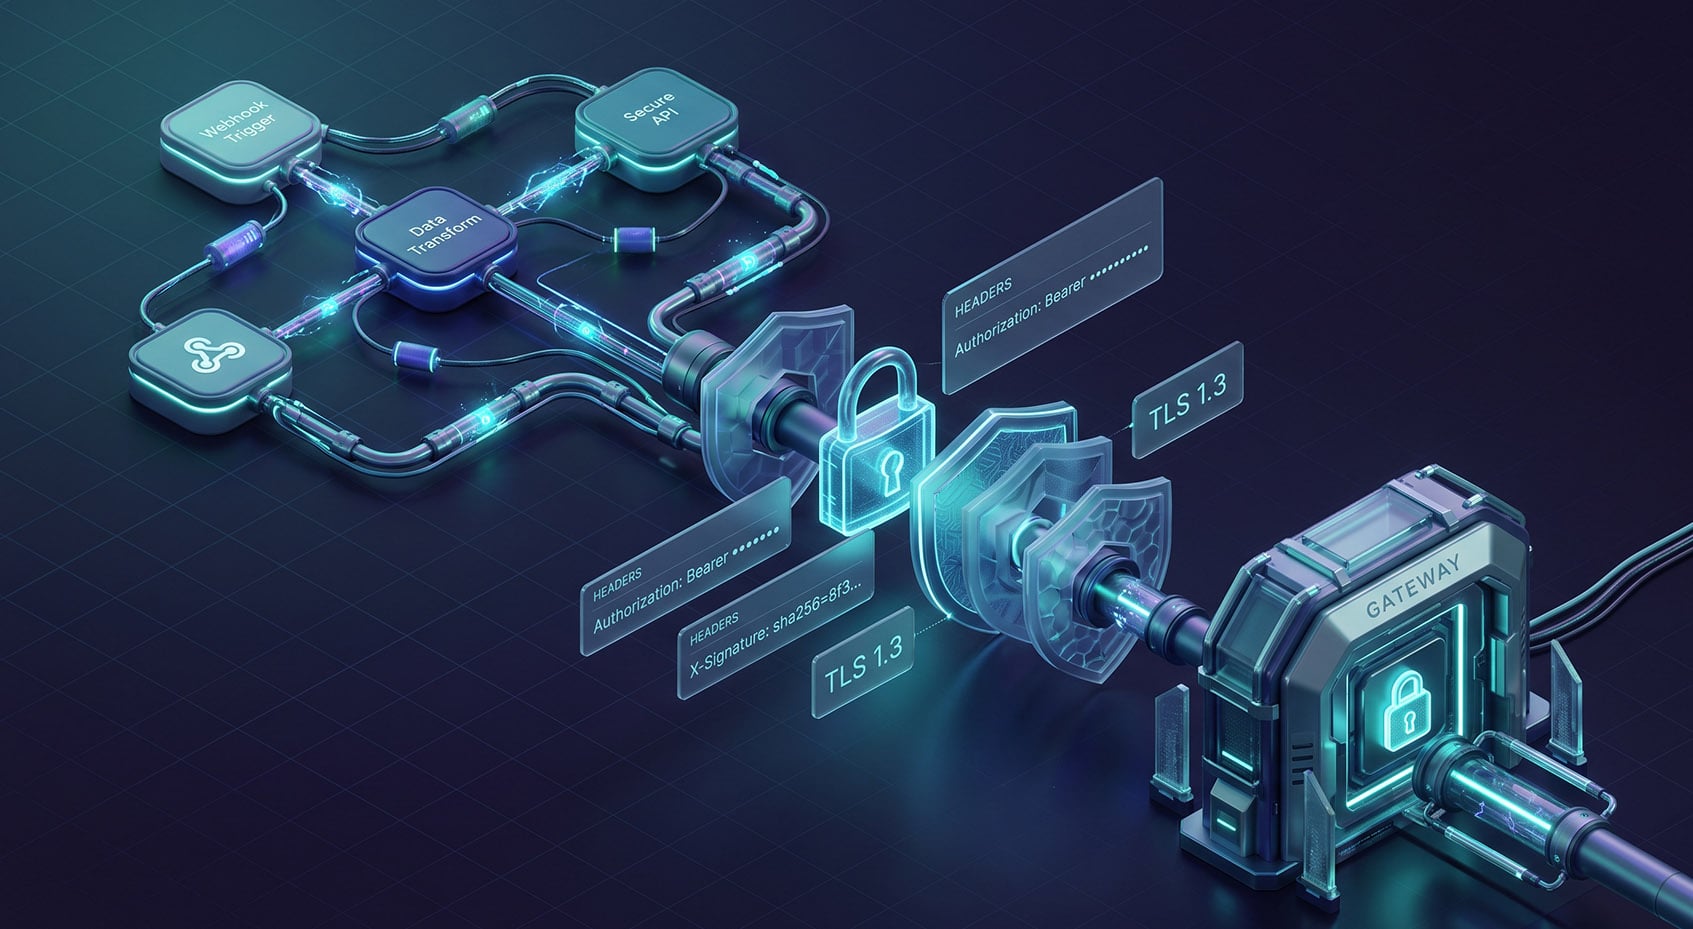
When you put n8n in production, your webhooks and API calls become part of your security boundary. Attackers know that a single unauthenticated endpoint or a leaked secret can trigger downstream actions—email blasts, database writes, or payment updates. This guide shows you how to harden n8n workflows with webhook authentication, secure API integration, and practical controls you can deploy today.
Executive Overview
The goal is simple: make automated workflow security a default, not an afterthought. You’ll learn how to protect n8n webhook endpoints, validate inbound requests, handle API credentials safely, and reduce the blast radius of mistakes. We’ll use n8n features (Webhook node, Credentials, Crypto/Code/IF nodes) plus proven infrastructure controls (TLS, mTLS, firewalls, rate limits).
Security Blueprint for n8n Webhooks and APIs
Here’s the high-level approach you can adapt to your stack:
- Authenticate every webhook (Basic or Header auth at minimum).
- Verify signatures (HMAC) or tokens (JWT/introspection) inside the workflow.
- Terminate TLS and, where possible, enforce mutual TLS (mTLS) at the reverse proxy.
- Restrict methods and IPs; add rate limiting and WAF rules.
- Keep credentials out of logs; rotate and store them securely.
- Validate payloads and block replays to stop duplicated or forged events.
Quick Comparison: Threats vs Controls
| Threat |
Primary Control |
How to Implement in n8n/Infra |
| Unauthenticated webhook calls |
Webhook authentication |
Set Webhook node “Authentication” to Basic or Header; validate secret/token |
| Forged payloads |
HMAC/JWT verification |
Crypto + Code/IF nodes to verify HMAC; or IdP introspection for JWT |
| Credentials leakage |
Secrets management |
Use n8n Credentials, env vars, N8N_ENCRYPTION_KEY; avoid hardcoding |
| Replay attacks |
Nonce/timestamp checks |
Validate timestamp; use Redis node to reject duplicate IDs with TTL |
| Brute force / DoS |
Rate limits & IP allowlists |
Nginx/Cloudflare rate limiting; firewall provider IPs only |
| Man-in-the-middle |
TLS / mTLS |
Terminate TLS; optionally require client certs at proxy |
1) Lock Down Your n8n Webhook Endpoints
Start with authentication at the edge of each inbound flow.
Use Webhook Node Authentication
- Basic Auth: Good for first-line protection. Create Basic Auth credentials in n8n and attach them to the Webhook node.
- Header Auth: Provide a custom header name/value (for example, X-Webhook-Secret). Ideal when the sender supports static secrets.
How to Fix It:
- Open your Webhook node in n8n.
- Set Authentication to Basic or Header.
- Create/select credentials (store the secret in Credentials, not in plain text).
- Limit HTTP Method to only what you need (often POST).
Tip: Don’t expose the test URL in production. Always use the production webhook URL, and share it only with trusted systems.
Enforce TLS and Prefer mTLS for High-Risk Flows
Always use HTTPS. For sensitive integrations (payments, internal systems), add mutual TLS at your reverse proxy so only clients with valid certs can reach n8n.
Nginx mTLS Example:
 server {
   listen 443 ssl http2;
   server_name workflows.example.com;

   ssl_certificate     /etc/ssl/certs/fullchain.pem;
   ssl_certificate_key /etc/ssl/private/privkey.pem;

   # Require client certs (mTLS)
   ssl_client_certificate /etc/nginx/client_cas.pem;
   ssl_verify_client on;

   # Rate limit requests to webhooks (tune values for your traffic)
   limit_req_zone $binary_remote_addr zone=api_rate:10m rate=5r/s;

   location /webhook/ {
     limit_req zone=api_rate burst=20 nodelay;
     proxy_set_header X-Forwarded-Proto https;
     proxy_set_header X-Forwarded-For $remote_addr;
     proxy_pass http://n8n:5678;
   }
 }
2) Verify Signatures and Tokens (Stop Forgery)
Authentication at the URL level is not enough. Validate that the request body wasn’t tampered with. Two common patterns are HMAC signatures and JWTs.
HMAC Signature Verification
Many providers (Stripe, GitHub, etc.) sign payloads. You should independently compute the signature and compare.
How to Fix It (n8n pattern):
- Webhook node receives the request.
- Set node extracts headers and timestamps you need (e.g., X-Signature, X-Timestamp).
- Crypto node computes HMAC of the raw body using your shared secret (configure the same hash algorithm as the sender, e.g., SHA256).
- Code node performs a constant-time comparison and checks the timestamp is within tolerance (e.g., 5 minutes).
- IF node routes: valid → continue; invalid → respond 401/400 and stop.
Code Node: Constant-time compare + timestamp check
 // Run Once for Each Item
 const headerSig = $json.headers["x-signature"] || ""; // provider's signature
 const timestamp = Number($json.headers["x-timestamp"]) || 0; // seconds
 const now = Math.floor(Date.now() / 1000);

 // From previous Crypto node: computed HMAC hex in $json.computedHmac
 const computed = ($json.computedHmac || "").toLowerCase();
 const provided = (headerSig || "").toLowerCase();

 // Basic time-skew check (5 min window)
 if (Math.abs(now - timestamp) > 300) {
   return [{ json: { ok: false, reason: "stale timestamp" }}];
 }

 // Constant-time string compare
 function safeEqual(a, b) {
   if (typeof a !== 'string' || typeof b !== 'string') return false;
   let mismatch = a.length === b.length ? 0 : 1;
   const len = Math.max(a.length, b.length);
   for (let i = 0; i < len; i++) {
     const ca = a.charCodeAt(i) || 0;
     const cb = b.charCodeAt(i) || 0;
     mismatch |= ca ^ cb;
   }
   return mismatch === 0;
 }

 if (!safeEqual(computed, provided)) {
   return [{ json: { ok: false, reason: "bad signature" }}];
 }

 return [{ json: { ok: true } }];
Note: Make sure you compute the HMAC on the exact payload bytes the provider used. If the sender includes a prefixed string (e.g., timestamp.payload), replicate it before hashing.
JWT Validation (Two Practical Options)
- Token Introspection: If your IdP exposes an OAuth2 introspection endpoint, call it via an HTTP Request node, authenticate with client credentials, and ensure the token is active and has expected scopes/audience.
- Upstream Validation: Prefer validating JWTs at your API gateway or reverse proxy. Forward only verified requests to n8n to reduce complexity inside workflows.
How to Fix It (Introspection flow in n8n):
- Extract the Authorization header in a Set node.
- Use an HTTP Request node to POST to /oauth2/introspect with your client credentials.
- Use an IF node to check active === true and validate scope, aud, and exp.
3) Block Replays and Duplicate Events
Replay attacks resend a valid request to trigger actions multiple times. Protect with timestamps and one-time nonces or event IDs.
How to Fix It (Redis-based dedupe):
- Identify a unique ID from headers/body (e.g., Idempotency-Key or provider’s event ID).
- Use the Redis node to SETNX the key with a short TTL (e.g., 10 minutes).
- If the key already exists, return 409 Conflict and stop the workflow.
This simple pattern stops accidental replays and malicious duplicates.
4) Secure API Integration Outbound (HTTP Request Node)
When n8n acts as a client, it must protect your downstream APIs and credentials.
- Use Credentials: Store API keys, Basic, or OAuth2 in Credentials, not in the node parameters. Avoid hardcoding secrets in expressions.
- Don’t Ignore SSL: Keep Ignore SSL Issues disabled in production. Only use it for controlled dev scenarios.
- Principle of Least Privilege: Scope OAuth apps and API keys to the minimal permissions and resources.
- Rate Limits & Retries: Configure reasonable retry logic; respect provider rate limits to avoid bans and unexpected throttling.
- Payload Validation: Validate and sanitize data before sending to APIs. Use IF/Code nodes to enforce allowed values.
5) Credentials and Secrets Management
Credentials are encrypted at rest in n8n, but you still need to run the platform securely.
- Set N8N_ENCRYPTION_KEY: Always define a strong key in production so credentials are properly encrypted on disk.
- Use Environment Variables: Reference env vars in credentials/headers using expressions like {{$env.WEBHOOK_SECRET}} for easier rotation.
- Limit Access: Restrict who can view or edit Credentials. If you have team features, use roles and separate environments.
- Rotate Secrets: Regularly rotate API keys and shared secrets. Keep a short overlap window when changing providers’ webhook secrets.
6) Network Edge: IP Allowlisting, WAF, and Rate Limiting
Never rely on security by obscurity. Put controls in front of n8n:
- IP Allowlisting: If a provider publishes outbound IP ranges, allow only those to reach your webhook paths via firewall or Cloudflare rules.
- WAF Rules: Block common injections and enforce header presence (e.g., drop requests missing X-Webhook-Secret).
- Rate Limits: Throttle bursts to prevent resource exhaustion. Tailor limits per endpoint.
7) Workflow Hygiene: Minimize Data Exposure
Assume that data flowing through your workflow may be logged or stored during errors. Reduce exposure:
- Don’t log secrets: Avoid placing secrets in node parameters that appear in execution data. Keep them in Credentials.
- Limit saved data: In workflow settings, store only what you need (e.g., disable saving full success data for sensitive flows if it’s not required for debugging).
- Mask before persist: If you write to databases or tickets, mask tokens and PII in a Code/Function node first.
8) Real-World Implementation Examples
Example A: Stripe-style Webhook with HMAC + Replay Guard
- Webhook (POST; Header Auth with static secret).
- Set node pulls Stripe-Signature and id from body.
- Redis node: SETNX event:{id} with TTL 10m; if exists → respond 409.
- Crypto node: HMAC SHA256 of the signed payload string using env secret.
- Code node: constant-time compare of computed vs header; timestamp window check.
- IF node: valid → continue to business logic; invalid → return 400.
Example B: Internal API Webhook with mTLS + JWT Introspection
- Nginx enforces mTLS and rate limits on /webhook/internal/.
- Webhook node (Header Auth optional) accepts only POST.
- Set node extracts bearer token from Authorization header.
- HTTP Request node calls your IdP’s /oauth2/introspect using client credentials stored in n8n Credentials.
- IF node checks active === true and required scopes before proceeding.
Common Pitfalls to Avoid
- Relying on obscurity: Unique webhook URLs aren’t a substitute for authentication and signature checks.
- Disabling SSL verification: Leaving “Ignore SSL Issues” on in production undermines API endpoint protection.
- Storing secrets in nodes: Keep secrets inside Credentials or env vars to prevent accidental exposure.
- No replay protection: Without timestamp/nonce checks, valid requests can be abused repeatedly.
- Over-permissioned tokens: API keys and OAuth apps should have the least privilege needed for the task.
Future Outlook and Strategic Takeaway
Automation will keep moving closer to core systems—billing, HR, customer data. That’s why automated workflow security must be part of your engineering checklist. Build a repeatable pattern: webhook authentication, request verification, network controls, and careful credential handling. Once templatized, teams can ship secure n8n workflows quickly without reinventing the wheel each time.
FAQ
How do I secure an n8n webhook quickly?
Enable Basic or Header authentication in the Webhook node, restrict the HTTP method, and place the instance behind HTTPS. Then add HMAC or token verification inside the workflow.
Is HMAC or JWT better for webhook authentication?
They solve different problems. HMAC verifies payload integrity with a shared secret. JWT is a bearer token that can include claims and expiry. Use what your provider supports; for internal systems, JWT plus introspection at the edge is often cleaner.
Can I do mutual TLS (mTLS) with n8n?
Yes—terminate TLS and enforce mTLS at your reverse proxy (e.g., Nginx, Cloudflare, API gateway). Only forward verified requests to the n8n webhook path.
How should I store secrets in n8n?
Use Credentials and reference environment variables when possible. Set N8N_ENCRYPTION_KEY in production and avoid hardcoding secrets in node parameters or expressions.
Final Thoughts
Strong n8n security is about layers: authenticated endpoints, verified payloads, protected networks, and careful secret handling. Put these patterns into a template workflow and roll them out across your automations.
Need help implementing this? Looking to automate your workflows with AI and n8n? Explore AI Integration & n8n Automation Services to build reliable, production-ready automations that actually work.