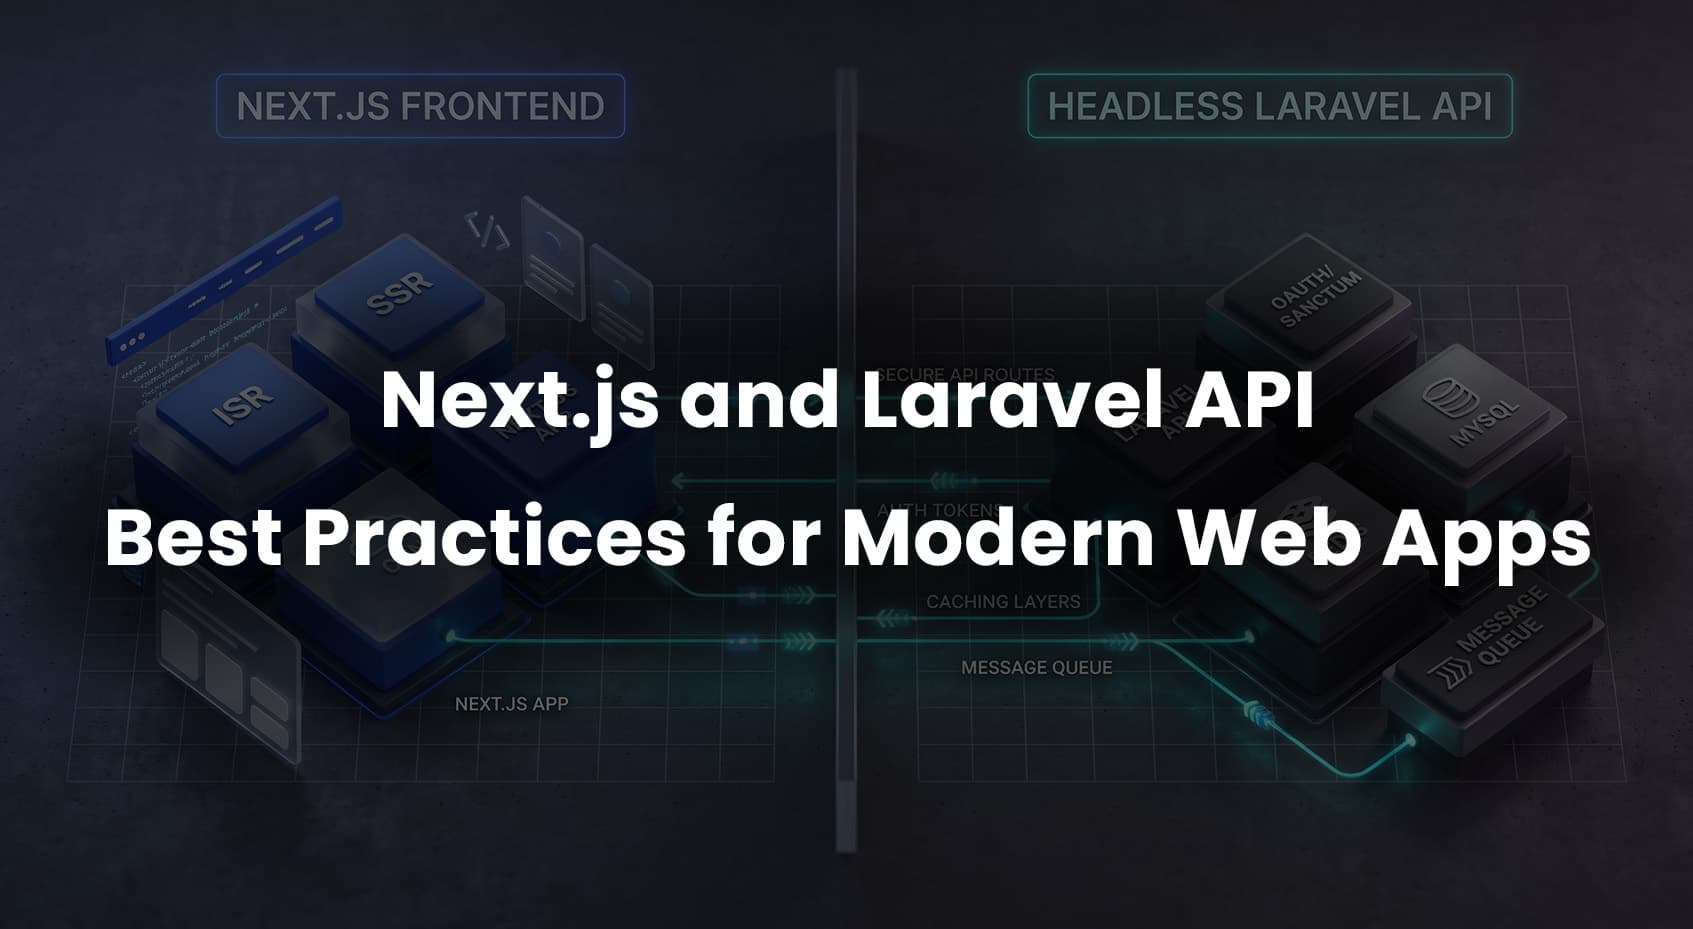
If you’re building a modern full stack development project, pairing a Next.js frontend with a headless Laravel API is a strong choice. You get React-based UX, SEO-friendly SSR/ISR, and Laravel’s mature routing, Eloquent, queues, and first-class DX. The challenge is bridging them cleanly: authentication, caching, performance, and deployment decisions can make or break your app.
This guide shows you exactly how to connect Next.js to a Laravel API, step-by-step. You’ll learn authentication options (Sanctum, Passport/OAuth, JWT), SSR/ISR strategies, caching, file uploads, testing, and production deployment patterns. The goal: a stable, fast, secure decoupled architecture you can scale.
Executive Overview
What we’re solving: build a decoupled architecture where Next.js drives UI/SEO and a headless Laravel API powers core business logic. Key decisions include how the browser authenticates (cookies vs tokens), how Next.js fetches data for SSR/ISR/CSR, how to structure responses, and how to deploy both sides safely.
Core thesis: treat Laravel as a clean, versioned API and treat Next.js as the consumer with clear caching, error handling, and security boundaries. Optimize for DX without compromising security.
Architecture: Start With Clear Boundaries
- API-first Laravel (Headless Laravel): Use API routes exclusively. Format responses consistently (Resources or JSON:API). Keep controllers thin; push rules to Form Requests and Services.
- Next.js App Router: Use Server Components for data-heavy UI, Route Handlers for proxying and secret work, and Client Components only where interactivity is mandatory.
- Domains: If you can, run both under the same top-level domain (e.g., app.example.com and api.example.com) to simplify cookies and CSRF with Sanctum. If cross-domain, prefer OAuth or stateless JWT.
Data Contract: Respond Consistently
- Resources/Transformers in Laravel for stable JSON shapes. Avoid leaking DB structure directly.
- Pagination: Standardize on Laravel’s paginator JSON or JSON:API pagination.
- Dates & Timezones: Return ISO 8601 in UTC. Convert on the client.
- Versioning: Prefix routes, e.g., /api/v1. Don’t break contracts silently.
Authentication Patterns That Work
Choosing the right authentication affects security, SSR, and cookies. Here are three proven patterns for Laravel API authentication Next.js:
1) Cookie-Based Sessions with Laravel Sanctum (Best if Same Top-Level Domain)
Great DX for SPAs/SSR with first-party cookies and CSRF protection. Works best when Next.js and Laravel share a TLD.
Laravel Setup:
- Install Sanctum and configure stateful domains.
- Enable CORS for your Next.js origin.
- Expose sanctum/csrf-cookie, then login with credentials.
 # .env (Laravel)
 SESSION_DRIVER=cookie
 SANCTUM_STATEFUL_DOMAINS=app.example.com
 SESSION_DOMAIN=.example.com
 APP_URL=https://api.example.com
 // routes/api.php
 Route::middleware('auth:sanctum')->get('/user', fn (Request $request) => $request->user());

 // routes/web.php or api.php (login)
 Route::post('/login', function (Request $request) {
     $credentials = $request->validate([
         'email' => 'required|email',
         'password' => 'required'
     ]);

     if (!Auth::attempt($credentials)) {
         return response()->json(['message' => 'Invalid credentials'], 422);
     }

     $request->session()->regenerate();
     return response()->json(['message' => 'ok']);
 });
Next.js (Server Component) Example:
- Call /sanctum/csrf-cookie (with credentials) to initialize CSRF.
- POST /login with X-XSRF-TOKEN.
- Subsequent requests send session cookie automatically.
 // app/(auth)/login/action.ts
 "use server";

 export async function login(email: string, password: string) {
   const base = process.env.LARAVEL_API_URL!; // https://api.example.com

   // 1) Get CSRF cookie
   await fetch(`${base}/sanctum/csrf-cookie`, {
     method: 'GET',
     credentials: 'include',
     headers: { 'Accept': 'application/json' },
     cache: 'no-store'
   });

   // 2) Get XSRF token from cookie storage if proxying through a Route Handler
   // If calling cross-domain directly from the browser, axios/fetch will read XSRF cookie automatically.

   // 3) Login
   const res = await fetch(`${base}/login`, {
     method: 'POST',
     credentials: 'include',
     headers: {
       'Content-Type': 'application/json',
       'Accept': 'application/json',
       // If proxying through Next Route Handlers, set X-XSRF-TOKEN from cookie value
     },
     body: JSON.stringify({ email, password })
   });

   if (!res.ok) throw new Error('Login failed');
 }
When to use: Same-site or subdomain deployments, need SSR with built-in CSRF, and want Laravel’s session ergonomics.
2) OAuth 2.0 with Laravel Passport + NextAuth (Best Cross-Domain, SSO-Friendly)
Make Laravel the OAuth provider (Passport). NextAuth in Next.js handles the OAuth dance. You get refresh tokens and can integrate SSO providers later.
Steps:
- Enable Passport and create a Password or Authorization Code client.
- Expose standard OAuth endpoints (/oauth/authorize, /oauth/token, /oauth/userinfo).
- Configure NextAuth with a custom OAuth provider pointing to Laravel.
 // app/api/auth/[...nextauth]/route.ts
 import NextAuth from 'next-auth';
 import OAuthProvider from 'next-auth/providers/oauth';

 const handler = NextAuth({
   providers: [
     OAuthProvider({
       id: 'laravel',
       name: 'Laravel',
       clientId: process.env.LARAVEL_OAUTH_CLIENT_ID!,
       clientSecret: process.env.LARAVEL_OAUTH_CLIENT_SECRET!,
       wellKnown: `${process.env.LARAVEL_API_URL}/.well-known/openid-configuration`,
       authorization: { params: { scope: 'openid profile email' } },
     })
   ],
   callbacks: {
     async jwt({ token, account }) {
       if (account?.access_token) token.accessToken = account.access_token;
       return token;
     },
     async session({ session, token }) {
       session.accessToken = token.accessToken as string;
       return session;
     }
   }
 });

 export { handler as GET, handler as POST };
When to use: Different domains, complex auth needs, mobile clients, or SSO. Clear separation: Next.js stores tokens (usually in an encrypted cookie) and attaches Bearer tokens to API requests server-side.
3) Stateless JWT (Simple, Flexible, Handle With Care)
Laravel issues a JWT (e.g., via tymon/jwt-auth or custom). Next.js stores it in an httpOnly cookie using a Route Handler to avoid exposing tokens to the browser.
 // app/api/login/route.ts (Next.js)
 import { cookies } from 'next/headers';

 export async function POST(req: Request) {
   const { email, password } = await req.json();
   const res = await fetch(`${process.env.LARAVEL_API_URL}/api/v1/login`, {
     method: 'POST',
     headers: { 'Content-Type': 'application/json' },
     body: JSON.stringify({ email, password }),
     cache: 'no-store'
   });
   if (!res.ok) return new Response('Unauthorized', { status: 401 });
   const { token } = await res.json();

   cookies().set('token', token, { httpOnly: true, secure: true, sameSite: 'lax', path: '/' });
   return new Response('ok');
 }
When to use: Multi-client APIs where sessions aren’t needed. Plan token rotation and revocation.
Rendering & Data Fetching: SSR, ISR, CSR
- SSR (Server-Side Rendering): Good for dynamic, personalized pages. Fetch in Server Components or Route Handlers. Keep secrets on the server.
- ISR (Incremental Static Regeneration): Mix of performance and freshness for mostly static content (blogs, docs). Use revalidate times or tag-based revalidation.
- CSR (Client-Side Rendering): For highly interactive dashboards after initial auth. Avoid moving secrets to the client.
 // app/products/page.tsx (Server Component with ISR)
 export const revalidate = 60; // ISR every 60s

 export default async function ProductsPage() {
   const res = await fetch(`${process.env.LARAVEL_API_URL}/api/v1/products`, {
     next: { revalidate: 60, tags: ['products'] },
     headers: { 'Accept': 'application/json' }
   });
   if (!res.ok) throw new Error('Failed to load products');
   const data = await res.json();
   return (
     <div>{data.data.map((p: any) => (<div key={p.id}>{p.name}</div>))}</div>
   );
 }
API-Driven Invalidation: From Laravel, on product update, hit a protected Next.js route that calls revalidateTag('products') to refresh cached pages instantly.
Performance & Stability
- Avoid N+1: Use with() and loadMissing() in Eloquent. Add indexes.
- HTTP Caching: Return ETag and Cache-Control. Next.js respects conditional requests; save bandwidth with If-None-Match.
- Pagination: Always paginate large lists. Expose total counts sparingly (can be expensive).
- Rate Limiting: Throttle middleware in Laravel; backoff/retry on the Next.js side for transient errors.
- Timeouts: Set short timeouts in Next fetches to avoid hanging SSR.
 // Example Laravel Resource with ETag
 return response()->json($payload)
     ->setEtag(sha1(json_encode($payload)))
     ->setCache(['etag' => true, 'max_age' => 60, 'public' => true]);
File Uploads: Do Not Pipe Large Files Through Your API
Use pre-signed URLs from Laravel; upload directly to S3 from Next.js. This keeps your API fast and reduces egress costs.
 // Laravel: generate pre-signed URL
 use Illuminate\Support\Facades\Storage;

 Route::post('/uploads/sign', function (Request $request) {
     $request->validate(['filename' => 'required|string']);
     $path = 'uploads/'.uniqid().'_'.$request->filename;
     $url = Storage::disk('s3')->temporaryUploadUrl($path, now()->addMinutes(5));
     return response()->json(['url' => $url, 'path' => $path]);
 })->middleware('auth:sanctum');
 // Next.js: upload directly to S3 using the signed URL
 export async function uploadFile(file: File) {
   const signRes = await fetch('/api/sign', { method: 'POST', body: JSON.stringify({ filename: file.name }) });
   const { url, path } = await signRes.json();
   const put = await fetch(url, { method: 'PUT', body: file });
   if (!put.ok) throw new Error('Upload failed');
   return path;
 }
Real-Time Updates
- Laravel Echo + Pusher/Ably: Broadcast from Laravel events; subscribe in Next.js client components.
- Server-Sent Events (SSE) or WebSockets: Use if you need low-latency dashboards.
Keep secrets server-side; only expose public keys in the client.
Testing & Quality Gates
- Contract Tests: Define OpenAPI in Laravel and validate in CI. Prevent breaking changes.
- Pest (Laravel): Feature tests for endpoints, auth, policies.
- Playwright (Next.js): E2E flows hitting the real API (staging).
- Consumer-Driven Contracts (Optional): Tools like Pact to catch schema drift.
Deployment Patterns
- Vercel (Next.js) + Forge/Vapor (Laravel) is common. Pin LARAVEL_API_URL in Vercel envs. Use HTTPS everywhere.
- Same TLD for Sanctum: Configure cookie domain to .example.com. Add CORS origins and stateful domains correctly.
- Proxy Route Handlers: For JWT/OAuth, proxy authenticated requests through Next.js Route Handlers to attach tokens server-side.
- Observability: Use Sentry/New Relic on both sides. Propagate a X-Request-ID from Next.js to Laravel for tracing.
Common Pitfalls (and How to Fix Them)
1) CORS and CSRF Confusion
Problem: Requests fail with 419/403 or preflight errors.
How to Fix It:
- For Sanctum, call /sanctum/csrf-cookie first and send withCredentials.
- Set SANCTUM_STATEFUL_DOMAINS and SESSION_DOMAIN properly.
- Set allowed Access-Control-Allow-Origin and Allow-Credentials to your Next.js domain.
2) Leaking Secrets to the Client
Problem: Tokens appear in browser devtools.
How to Fix It: Fetch from Server Components or Route Handlers only. Store tokens in httpOnly cookies via Next.js API routes, not localStorage.
3) Slow SSR Due to N+1 Queries
Problem: SSR waterfalls because the API is slow.
How to Fix It: Eager load relations, add DB indexes, introduce Redis caching, and use ISR where content is mostly static.
4) Inconsistent Date/Number Formatting
Problem: Different formats across pages.
How to Fix It: Always return ISO 8601 UTC from Laravel. Format in Next.js with Intl.DateTimeFormat or libraries like dayjs.
Quick Decision Table
| Decision |
Use When |
Pros |
Cons |
| Sanctum (cookies) |
Same TLD, SSR, SPA security |
Simple, CSRF built-in, great DX |
Trickier cross-domain |
| Passport + NextAuth (OAuth) |
Cross-domain, SSO, mobile |
Standards-based, refresh tokens |
More moving parts |
| JWT (custom) |
Stateless APIs, many clients |
Simple infra, no session store |
Token rotation/revocation needed |
| SSR |
Personalized, fast TTFB |
SEO + dynamic data |
Server load, careful caching |
| ISR |
Mostly static content |
Scales well, fresh enough |
Stale window between revalidations |
Example: A Clean Request Flow
- User visits /dashboard (Next.js SSR). Route Handler checks session/token, fetches /api/v1/me from Laravel.
- Laravel returns user with roles/permissions. Eager loads required relations.
- Next.js renders the page server-side and streams HTML. Client hydrates only interactive widgets.
- Client actions (filters, tabs) call Next Route Handlers, which attach tokens and call Laravel. No secrets in the browser.
Security Checklist
- Always use HTTPS. Set secure cookies and SameSite appropriately.
- Validate and sanitize input on the API; don’t trust the frontend.
- Rate-limit auth and mutation endpoints.
- Return minimal error messages on auth/permission failures.
- Implement Policies in Laravel; enforce authorization server-side.
Future Outlook
- Next.js Server Actions will reduce custom API routes for mutations, but keep your Laravel API as the source of truth.
- Edge Runtime is excellent for low-latency reads; ensure your Laravel API supports fast, cacheable endpoints.
- Laravel Reverb/WebSockets make real-time features simpler; combine with ISR and client hints for hybrid UX.
FAQ
Is Sanctum or Passport better for a Next.js Laravel API?
Use Sanctum if both apps share a top-level domain and you want cookie-based sessions with CSRF. Use Passport (OAuth) for cross-domain setups, mobile apps, or SSO. JWTs work too but require careful rotation and revocation planning.
How do I handle SSR without exposing tokens?
Fetch data in Next.js Server Components or Route Handlers. Store tokens in httpOnly cookies set by Next.js API routes. Never put tokens in localStorage or expose them to client components.
What’s the best way to cache pages and API responses?
Use Next.js ISR or tag-based caching for pages. On the API, use ETags and Cache-Control. For data-heavy queries, add Redis caching in Laravel. Trigger revalidation from Laravel after writes.
How do I upload files safely?
Generate pre-signed S3 URLs from Laravel and upload directly from Next.js. Don’t send large files through your API or Next.js server.
Final Thoughts
Bridging Next.js with a headless Laravel API works best when you define clear contracts, pick the right auth strategy for your domain setup, and treat caching as a first-class concern. Start with Sanctum on same-domain projects, use OAuth with NextAuth for cross-domain and SSO, and fall back to JWT when you need a lightweight stateless model. Pair SSR/ISR thoughtfully, standardize your responses, and automate testing to keep shipping safely.
Need help building or refactoring your full-stack web application? I build production-grade, API-driven systems engineered for speed, secure authentication, and seamless scaling. Reach out to review your setup or start a new project. Build Your Web Application